Monthly subscription · one panel · 24/7 monitoring · credit system
Active Defense Program.
Traditional security products are bought, installed and frozen at the level of the day they went live. The Active Defense Program re-measures, tests and scores your organisation's digital surface every month — and turns it into a concrete security score you can present to management.
Five components
Five components on a monthly rhythm, closed with one executive report.
Web surface scan
Everything you have published, seen the way an attacker sees it.
Vulnerability assessment
CVE-based detection across the full CVE and NVD catalogues, CVSS prioritisation, verification of closed findings.
Phishing simulation
Department-level scenarios that measure the human factor instead of guessing it.
Threat intelligence
Dark web, forums and leak platforms watched for your domains and credentials.
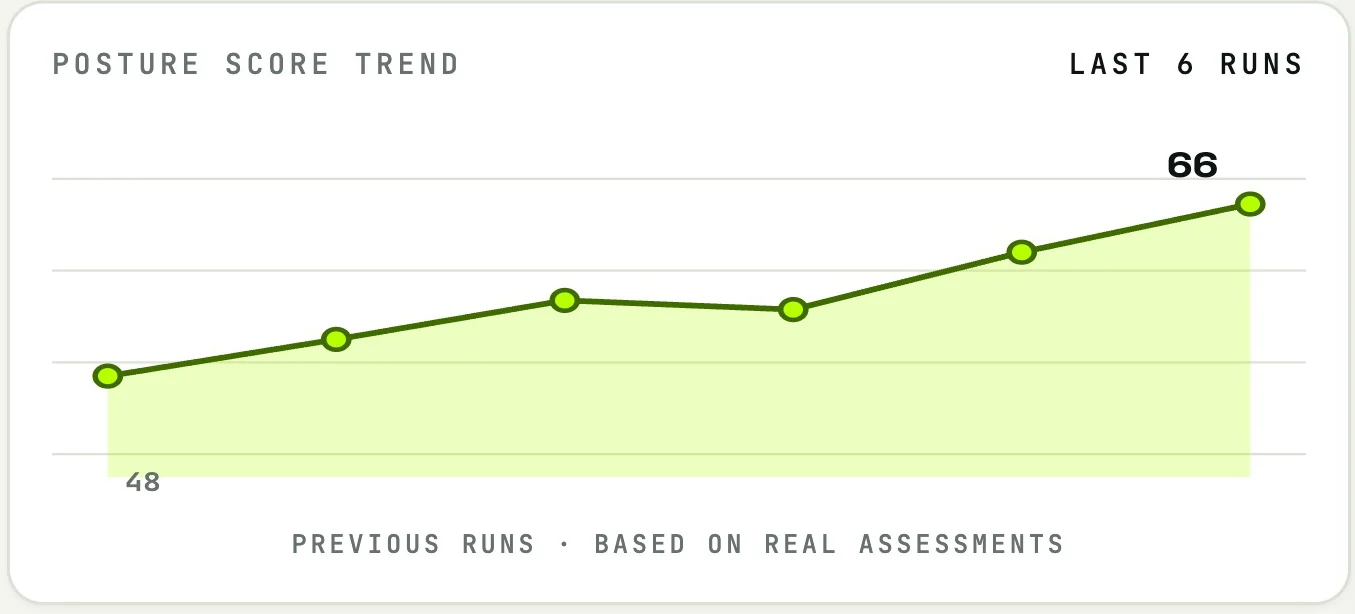
Watcher posture score
All of it in one number, one trend line and one report.
Monthly operating cycle
Repeated every month.
Each cycle ends where the next one starts: the improvement step re-measures what was fixed, so progress is proven rather than claimed.
- 01ScanSurface and assets
- 02TestVulnerabilities and the human factor
- 03DetectLeaks and risk
- 04ReportEvidence you can show
- 05ImproveRe-measure at month end
The classic approach
- A penetration test once a year; the report stays in a folder.
- A service opened the next month sits exposed without anyone knowing.
- Employee awareness is not measured; you learn about it when a breach happens.
- There is no concrete indicator to present to management.
- The leak is heard from a third party months later.
Active Defense Program
- Attack surface and vulnerabilities are re-measured every month.
- New services and subdomains are reported the month they are discovered.
- The human factor is measured with department-level phishing.
- Progress is proven with the Watcher posture score and its delta curve.
- 24/7 CTI monitoring raises an alert the moment a leak surfaces.
What leadership sees
One number a month, and the reason it moved.
Every month ends with an executive report: the score, the trend, what was closed, what is new and what to do next — written so that business and technical readers can both act on it.
Who it is for
Three reasons to run security on a monthly rhythm.
Companies with in-house IT
Reduce the load of recurring scanning, testing and reporting so your team can focus on remediation.
Audited organisations
Anyone who must produce regular evidence for ISO 27001, SOC 2, NIS2, cyber insurance or customer contracts.
MSSPs and solution partners
Deliver managed security under your own brand and build recurring revenue.
Your attack surface changed this week. Your last report didn't.
Start with a free assessment: we map your external attack surface and produce your first posture score.
No installation · no credit card · credit-based start