Dark web and forum intelligence
Dark web marketplaces, hacker forums and Telegram channels scanned 24/7.
- Dark web and forum scanning
- Telegram channel monitoring
- Combolist and leak detection
- Instant breach alerts
Cyber threat intelligence · Digital risk protection
Leaked passwords, compromised devices, fake domains and posts on the dark web — the external risks that belong to your organisation are monitored 24/7 and gathered on one dashboard.
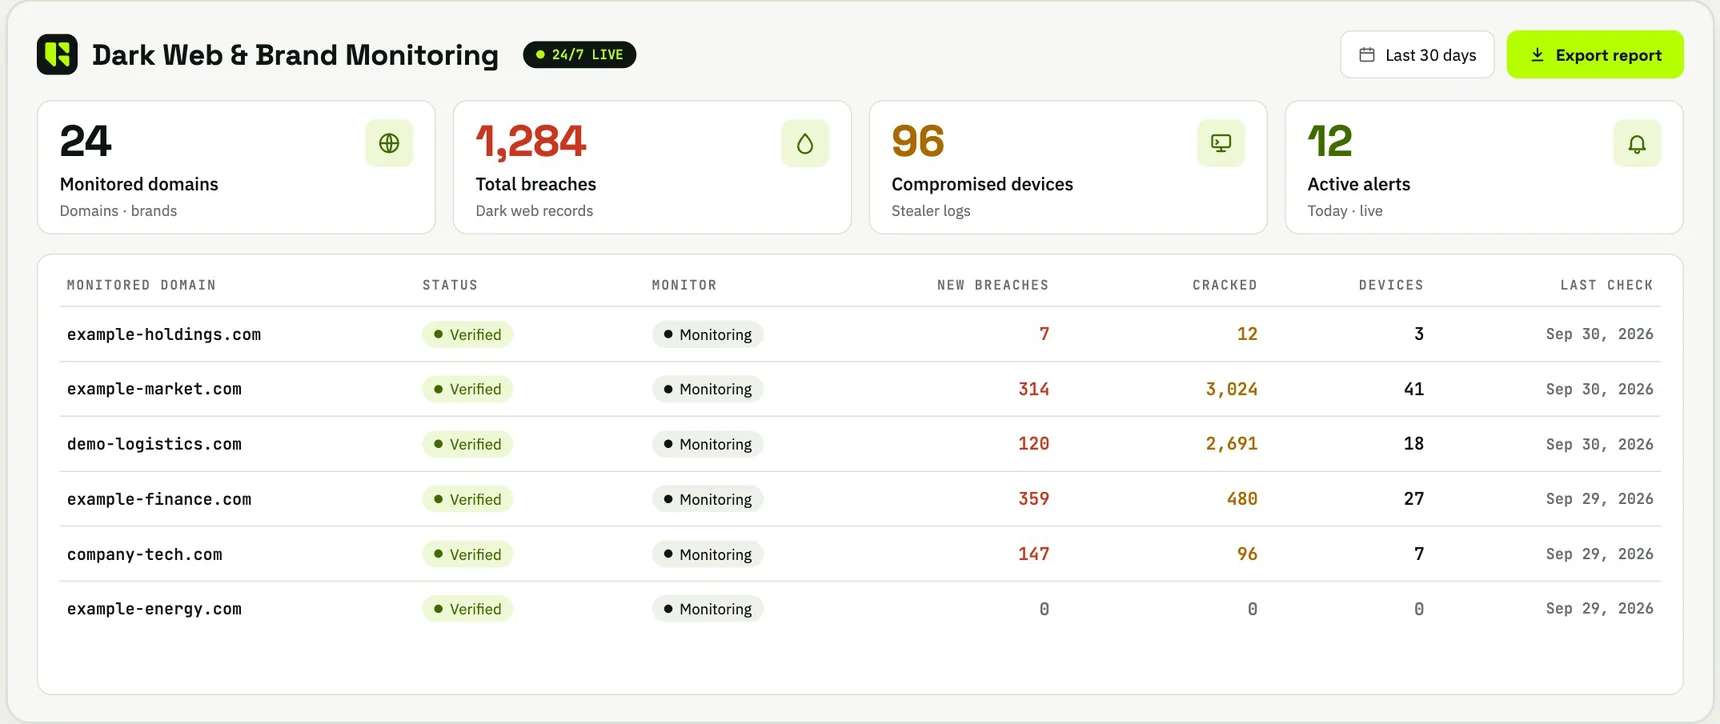
Dark web and brand monitoring
Domains are verified once. From then on, new breach records, cracked passwords and compromised devices tied to each domain appear here — with the date of the last check.
Six modules
An alert is raised when new exposure linked to your organisation is identified.
Dark web marketplaces, hacker forums and Telegram channels scanned 24/7.
Leaked credentials tied to your domains and e-mail accounts.
Devices taken over by malware, found through stealer-log data.
Domains, phishing sites and digital imitations that resemble your brand.
Ransomware attacks, breach disclosures and the cyber agenda in one feed.
Targeted analysis on request, delivered as encrypted PDF reports.
In detail
Monitoring covers individual e-mail addresses as well as whole domains. Records stay masked until you unlock them.
Stolen credentials. Credentials stolen by malware from infected devices, with the site they were used on; username and password combinations circulating in combolists.
Leaked company data. With the breach source, e-mail address and name.
Lookalike domains. Omissions, hyphenations, homoglyphs and TLD swaps — with registration date, mail and certificate status, a risk rating and WHOIS. Repeated every night.
DNS and e-mail health. SPF, DMARC, DKIM and MX checks that flag configuration associated with impersonation.
A downloadable threat intelligence report for management and auditors.
With Watcher: a new breach record is matched against what the other services know about the same person and device — so an exposed password on an unpatched laptop, owned by someone who clicked the last phishing test, is raised first as an alarm.
Verify a domain and see the first findings in the demo. Records stay masked until you unlock them.