Alarm
24/7Immediate action needed — an exposed account, a live threat, a critical vulnerability.
Delivered by: voice call and email
Buguardian MSSP platform · Watcher micro SOC
Buguardian brings every security service for MSSPs, resellers and corporate IT teams into one panel. Watcher correlates their findings around the clock, warns you by voice call and email when something is critical, and writes down what to do next.
No installation · no credit card · credit-based start
Management panel
313 companiesUpcoming licence renewals
“Leaked password, no second factor. Reset the password and make ThreatAuthenticator mandatory.”
Three levels
Watcher prioritises every finding into one of three levels. You are never left with a list of a thousand rows — only with the next action and the reason for it.
Immediate action needed — an exposed account, a live threat, a critical vulnerability.
Delivered by: voice call and email
Risk to plan for this week — an unpatched server, a newly exposed service.
Delivered by: email with the steps to close it
How to get stronger this quarter — trends, weak spots, training needs.
Delivered by: AI-written executive report
How the micro SOC works
Most organisations do not lack security data. It is scattered across screens, inboxes and spreadsheets. Watcher reads all of it, per company, and turns it into one order of priority.
Findings from every Buguardian service are gathered per company, in one place.
Watcher joins the traces the same incident leaves in different services.
Every result is scored and classed as an alarm, a warning or an advisory.
What to do, who should do it and why it matters reaches you directly.
Correlation pipeline · refreshes every 30 s
Sample tenant · updated 08:26:25
Illustration of the Watcher pipeline for a sample company: 6,031 findings from exposure scans, threat intelligence, phishing simulation and endpoints are correlated into 1,492 unique findings, with 4,539 duplicates merged. Watcher classes them as 14 alarms sent by voice call and email, 66 warnings, 344 advisories and 1,068 logged items. After the fix, 39 are verified resolved, 41 remain tracked, and the monthly report shows a posture score of 66.
Correlation in practice
A finance user's password is being shared on a leak forum.
The same account has no second factor enrolled.
The account owner filled in the credential form in last month's test.
Reset the password, enforce ThreatAuthenticator on the account today and assign the user a short awareness module.
Voice call placed at 03:47 · steps sent by email
The platform
Each service works on its own. Used together, their findings meet in the same company record and Watcher puts them in a single order of priority. Start with the ones you need and add the rest later.
Network discovery, CVE and VAS analysis, EPSS and CISA KEV context, scheduled and authenticated scans.
Exposure services Web application scanningAutomatic subdomain discovery, web and cloud scanning, risk scoring and continuous monitoring.
Web scanning Threat intelligence · DRPDark web and forum monitoring, Telegram, stealer logs, combolists, typosquats and fake sites — 24/7.
Digital risk protection Phishing simulationRealistic scenarios, hundreds of ready-made templates in 10+ languages, per-person tracking and awareness trends.
Human factor Buguardian ManagementOne agent for remote management, patching, inventory and tickets.
Endpoint management ThreatAuthenticatorA second verification step on user logins, managed per company from the MSSP panel.
Multi-factor authentication Infrastructure auditsFirewall analysis graded A to F, read-only Active Directory and database health checks.
Audit the core AvailabilityUptime monitoring for business services, SSL and IP reputation checks, managed VPN.
Stay availableWatcher posture score
Watcher reads the results of every service, merges duplicates of the same problem and seats them in one risk model. The services keep running in their own screens; Watcher only reads them.
Six of seven categories measured. The unmeasured one is flagged as a blind spot and its weight is redistributed.
Figures are a sample, not customer data.
Product
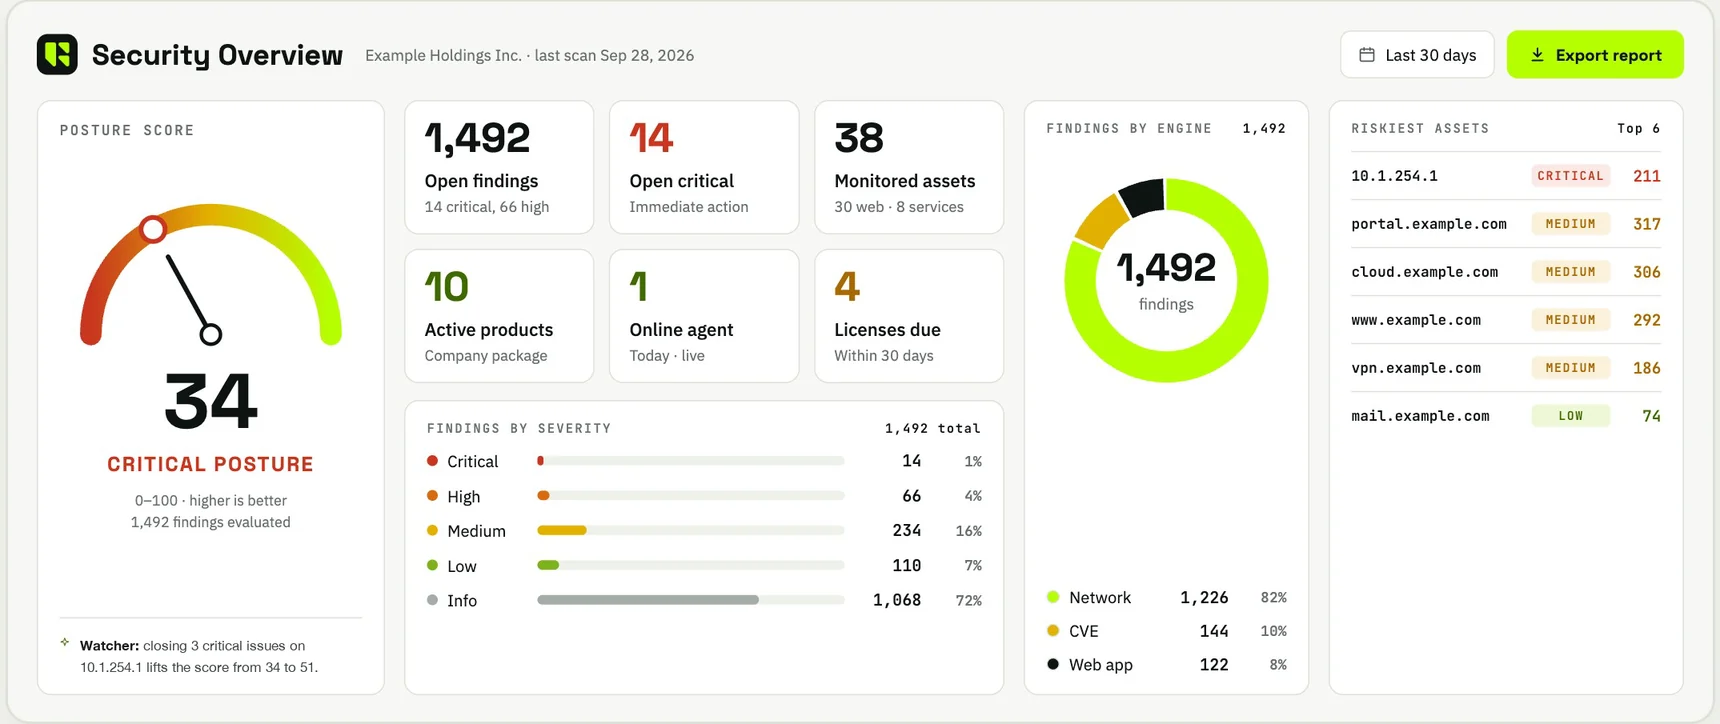
Posture score and band, open findings by severity, vulnerabilities that are actively exploited, services with a visibility gap, licences expiring within 30 days, and the five riskiest assets.
Why a micro SOC
Micro SOC means exactly this: Watcher watches 24/7, correlates, prioritises and calls you with the recommended steps. Action is taken by your team or your solution partner — with a ready road map in hand.
| Criterion | Your own SOC | Classic MSSP | Buguardian micro SOC |
|---|---|---|---|
| Time to start | Months, hiring | Weeks | Days |
| Staff needed | 5+ analysts | The provider's team | None for monitoring — your team takes the action |
| Coverage | Whatever you buy and integrate | The provider's tools | Exposure, identity, endpoint, data and people |
| What you receive | Logs and raw alerts | A monthly report | 24/7 alarms, warnings and advisories |
Active Defense Program
Traditional security products are bought, installed and frozen on the day they go live. The Active Defense Program re-measures your digital surface every month and turns it into a score you can put in front of management.
Who it is for
The team is already busy. Monitoring and reporting are handed over, so the team can focus on the fix.
Platform overviewAnyone who must produce regular evidence for ISO 27001, NIS2, GDPR, KVKK, cyber insurance or customer contracts.
Compliance mappingDeliver managed security under your own brand and turn one-off projects into recurring revenue.
Partner programme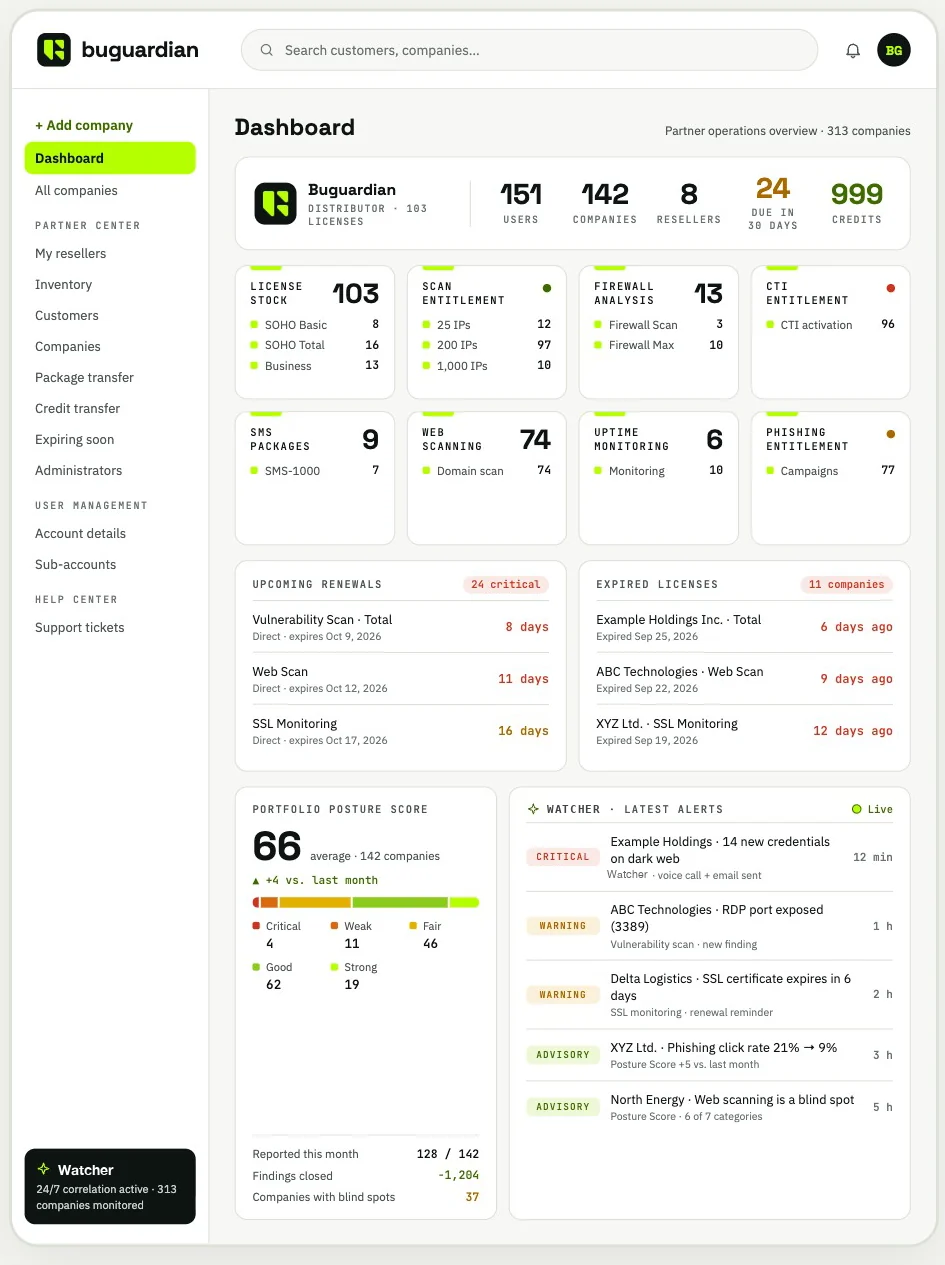
For partners
Add the Active Defense Program and Watcher to your existing service agreement. Raise your customers' security every month and invoice monthly. The whole operation runs on the Buguardian panel — you present it under your own brand.
Recurring revenue
A one-off sale becomes a monthly line item.
Your brand
Panel, report and notifications in your colours.
Credit-based
Pay for what you use, no infrastructure.
Zero extra headcount
Setup, monitoring and reporting sit with us.
Compliance
ISO 27001, NIS2, GDPR and KVKK do not ask for security to be set up once. They ask for it to be maintained and documented. Every Buguardian service produces dated evidence for a specific control.
Annex A controls and management system clauses: asset inventory, technical vulnerabilities, awareness, logging.
Govern, Identify, Protect, Detect — assets, risk assessment, awareness, continuous monitoring.
Article 21 risk measures, GDPR Article 32 regular testing and Articles 33–34 breach notification.
Türkiye: Article 12 data security obligations.
Questions
The questions IT managers and auditors ask us most often.
For internal network scans, one scanning appliance: an Ubuntu virtual machine with at least 4 cores, 8 GB of memory and 100 GB of disk. For inventory and patching, the endpoint agent on each machine. Web scanning, threat intelligence, certificate and blocklist monitoring start from a domain you verify with a DNS record.
No. The posture score is calculated deterministically from published weights. Watcher explains the score, connects related findings and recommends what to do first.
No. Every action is proposed with its reason and scope and runs only after an authorised person approves it. Actions go through the same controls as manual operations, and each one is recorded.
Yes. Distributors, solution partners and customers each have their own level, and every customer has an isolated workspace. One login covers all of them.
Threat pulse
Newly exploited vulnerabilities and joint advisories from CISA, refreshed every six hours, next to our own articles. Each card says what it means for your exposure.
3 Nov 2026 · 2 min read
Seven weighted categories, published weights and a deterministic calculation. Here is what goes into the number, and what never does.
4 Nov 2026 · CISA KEV
Apple iOS, iPadOS, macOS, Safari, tvOS and watchOS 10.5 contain an improper authentication vulnerability which could allow an attacker with arbitrary read and write capability to bypass pointer authentication.
Buguardian Vulnerability Management flags this with the CISA due date: 18 Nov 2026.
3 Nov 2026 · CISA KEV
WordPress WordPress Core contains a time-of-check time-of-use (TOCTOU) race condition vulnerability that could allow unauthenticated attackers to execute code on the server during the upgrade window. This is…
Buguardian Vulnerability Management flags this with the CISA due date: 6 Nov 2026.
Start with a free demo: we map a summary of your external attack surface and produce your first Watcher posture score.
No installation · no credit card · credit-based start